GitHub makes AI Scan for pull requests generally available, billed in AI Credits
The advisory, pull-request-only scanner is billed in Code Security AI Credits, including on public repositories, and targets languages CodeQL does not currently cover.
By BenchdictPublished Oct 30, 20264 min read
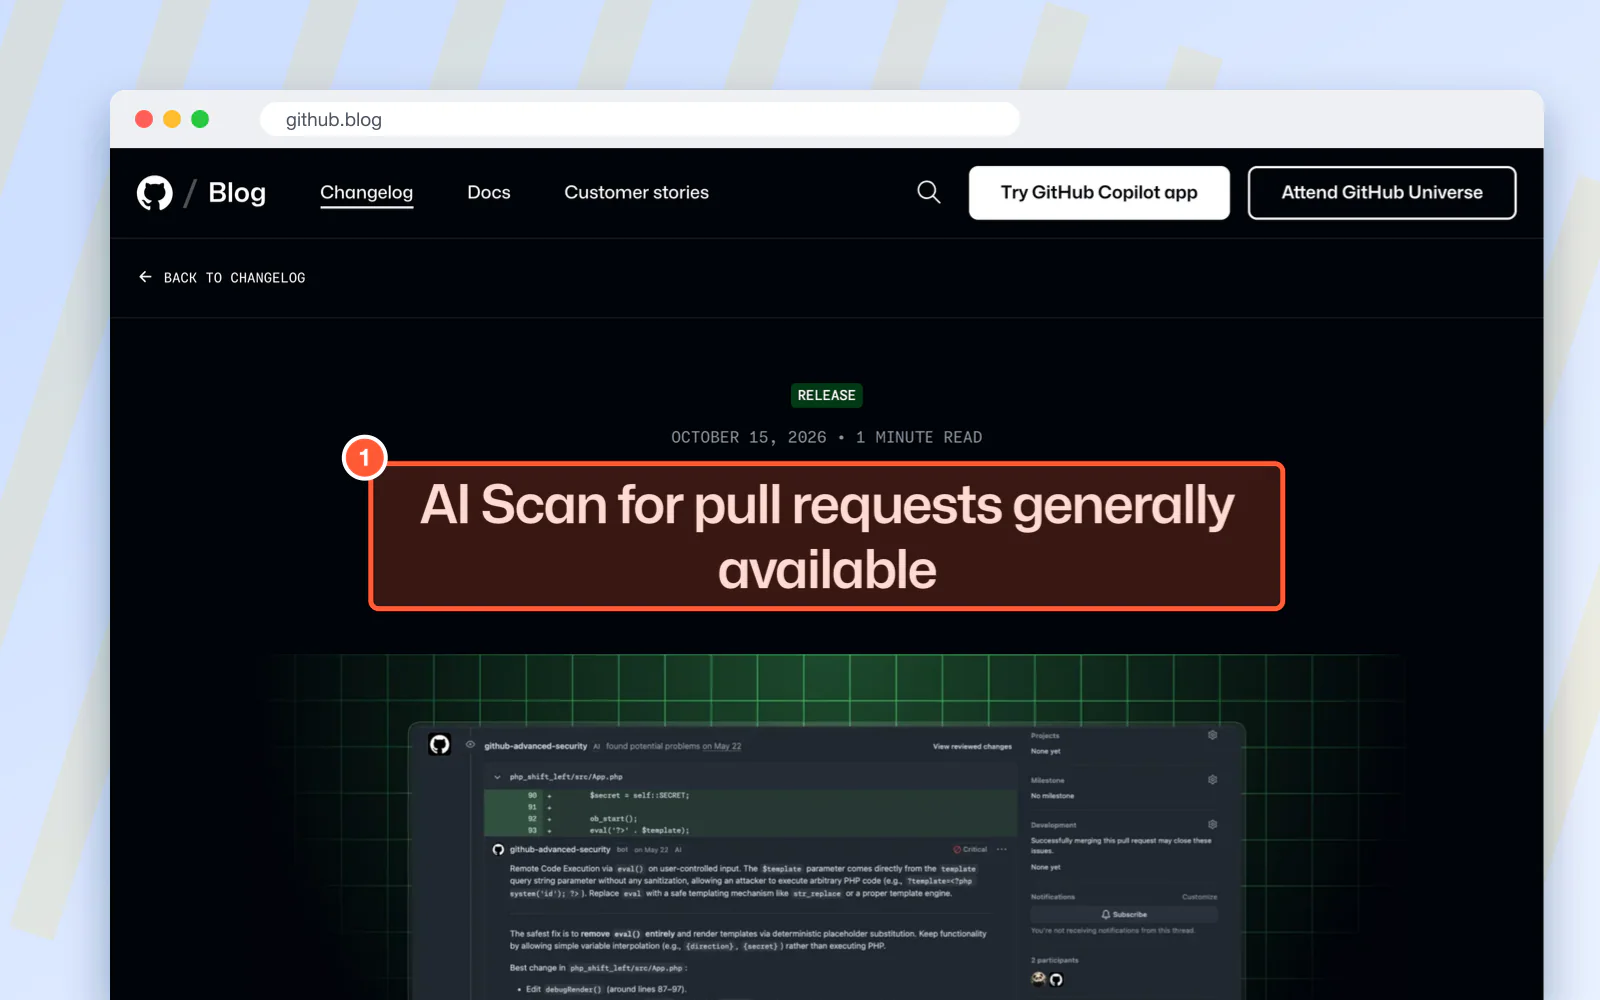
GitHub made AI Scan for pull requests generally available in code scanning on October 15, 2026. According to GitHub's documentation, enabling the organization setting applies it immediately to eligible repositories and can spend AI credits before repository admins opt out.
The feature itself is unremarkable: advisory findings beside CodeQL, with false positives GitHub warns about itself. The rollout is the story. An organization setting that switches on immediately and meters AI credits, even on public repositories, puts the burden on admins to opt out after spending may already have started. GitHub's own enterprise default is "not allowed", which is the clearest signal of how it expects cautious organizations to treat this: check the setting first, then decide whether advisory findings are worth a metered bill.
Key facts
- Status
- Generally available, announced 2026-10-15
- Findings
- Advisory: do not fail the code scanning check or block merges
- Billing
- Code Security AI Credits SKU, consumed even on public repos
- Rollout
- Org setting applies immediately to eligible repos; enterprise policy defaults to Not allowed
- Coverage
- Languages and frameworks CodeQL does not currently cover; list may change
- Eligible repos
- Public repos; private and internal org repos need GitHub Code Security or Advanced Security
- Copilot license
- Not required
- Not run on
- Fork pull requests and Dependabot pull requests
What GitHub released
GitHub's changelog says AI Scan now runs automatically on pull requests when code scanning and the repository's AI Scan setting are both enabled. Findings appear beside CodeQL results on the Conversation and Files changed tabs, marked with an "AI" indicator.
According to GitHub's documentation, AI Scan does not need a build system and may use code search to pull in repository context. Findings exist only on pull requests, not as backlog alerts, and full repository scans are not supported. The docs warn that findings may include false positives.

Cost and rollout
GitHub's billing documentation says AI Scan is billed under the Code Security AI Credits SKU, separate from active-committer licensing. It says the feature consumes these credits even on public repositories, which need no active-committer license. Credits included with a Copilot entitlement are used first; after that, usage is metered and governed by budgets.
GitHub's AI Scan documentation says a hard budget that leaves no credits means AI Scan cannot produce findings until the budget is raised or a new billing cycle starts.
The same documentation says the organization setting turns AI Scan on immediately for eligible repositories that have code scanning. For enterprises, the policy that allows AI Scan defaults to "Not allowed."
Next to CodeQL
GitHub describes AI Scan as a complement to CodeQL for languages and frameworks CodeQL does not currently handle, such as PHP, Shell/Bash, Terraform (HCL), Dockerfiles, JSP for Java and Blazor for C#; the list may change. Detection performance has not been published.
Who is affected
- Enterprise owners must allow the policy before any organization can enable it.
- Organization owners can then turn AI Scan on org-wide.
- Billing administrators hold the budgets that govern metered usage.
- Repository admins can opt out, but credits may already have been used.
Repositories in a managed user account's personal namespace are excluded. GitHub's pages do not describe an earlier preview, so what changed from pre-GA behavior is unconfirmed.
Sources
- AI Scan for pull requests generally availablePrimaryGitHub Changelog, Oct 15, 2026.What we took from it: GA date, automatic PR runs, AI indicator, eligibility, Copilot license, billing SKU, CodeQL language complement
- GitHub Advanced Security license billing - GitHub DocsDocsGitHub Docs, Oct 19, 2026.What we took from it: Credit use on public repos, order of included credits and metered budgets, managed-account exclusion
- AI Scan for pull requests - GitHub Enterprise Cloud DocsDocsGitHub Docs, Oct 19, 2026.What we took from it: Advisory findings, fork and Dependabot exclusions, PR-only scope, hard-budget behavior, immediate org rollout, enterprise default, false-positive caveat
Benchdict, Edited and published by Jason, Editor & Publisher. Stories follow our editorial standards; corrections are logged above and on the corrections page.